

Generative artificial intelligence and autonomous agents are introducing entirely new attack surfaces to enterprise IT, ranging from prompt injection to sensitive data leakage.
As autonomous agentic systems execute multi-step tasks across corporate platforms without constant human supervision, defining and enforcing behavioral guardrails has emerged as a critical challenge for organizations navigating this evolving landscape.
“Traditional web security expects a certain workflow,” says Jef Hu, Regional Manager and Security Sales Specialist APJ at Akamai Technologies, speaking on the sidelines of the VST ECS CXO Tech Summit.
“You have an input and you have an output; you inspect them. In this new era of agents and AI, agents may go out there and actually seek attacks. The copilot incident is a case in point, where an agent went to check an email, the email had a malicious payload, and it took the payload. It went to look out for attacks and actually processed it.”
Hu highlights a fundamental shift in technology risk. Where legacy web defenses rely on inspecting deterministic syntax, artificial intelligence operates on natural language semantics—a transition that renders traditional firewalls structurally unequipped for agentic security.
The fatal flaw of semantic attack surfaces
For decades, web application security relied on inspecting syntax patterns, such as parsing SQL statements or HTML tags. If an incoming request contained malicious syntax, web application firewalls could identify the pattern and block the payload immediately.
Generative AI breaks this defense paradigm entirely. Because AI models operate on natural language context, an attack can be structured in numerous ways without matching a traditional syntax signature.
“Web technology relies on syntax, whether it’s SQL or HTML,” Hu explains. “But in AI or generative AI, it’s based on semantic. You could say the same thing ten different ways. Not only that, when you carry out an attack, you can do it in many different prompts—almost like manipulation. That is one of the things that are different, and web security won’t be adequate to deal with it.”
This semantic vulnerability enables threats like memory poisoning and prompt injection, allowing attackers to manipulate agents into executing unintended background tasks. The challenge multiplies when autonomous agents interact across enterprise systems at machine speed.
“Enterprises continue to adopt agents in the organization to realize the benefits, but the challenge about agents is they will become your digital employees,” Hu notes.
“At the moment, we have great control over how employees are guided through HR processes and policies. But for agents, they operate at machine speed. You may have an intent for an agent to behave a certain way, but as we saw with Hugging Face and OpenAI, agents can decide to misbehave. What was scary is those agents were operating in the hundreds—close to 900 agents collaborating. It’s unprecedented.”
Enforcing zero trust and least privilege on autonomous agents
As autonomous agents gain broader system access, enterprise IT teams face the task of securing systems against both internal misbehavior and external exploitation.
“There are two types of agents: agents from the outside and agents on the inside,” Hu explains. “Regardless of what it is, from Akamai’s perspective, we are always in the path of the agent’s journey—from an end device or browser to the edge, to the APIs, and to the models. Throughout that journey, we have the ability to inspect critical signals like identity attribution, intent, and attacks, even before AI has the ability to reach the model and take reasoning.”
To prevent autonomous systems from executing unauthorized actions across enterprise software, organizations must enforce strict authorization controls and least privilege access.
“Architecting agents to follow certain frameworks and follow least privilege is super important,” Hu says. “If you don’t impose least privilege, you have situations like the Meta AI chatbot that was allowing attackers to reset passwords to Obama’s Instagram account because it had privileges beyond what it was supposed to have. We had incidents like Replit where, despite being instructed that this is a change freeze, the agent ended up deleting production databases. Was the agent supposed to have that privilege? Least privilege is mandatory. Think of it as zero trust; AI also needs that.”
The board-level impact: API execution and AI DDoS cost risks
As enterprise AI adoption expands, Application Programming Interfaces (APIs) have transitioned from simple data transfer channels into active execution vectors. Today, APIs serve as the primary mechanisms through which AI agents take real-world actions across corporate software.
This shift has elevated API security from a back-end IT issue directly into corporate boardrooms.
“APIs have been around for a really long time,” Hu states. “In the past, APIs were intended to be used for data transfer. What APIs are being used for nowadays is also to carry out actions. This has resulted in potential data leaks as well as malicious outcomes from those actions. When this happens, it becomes a business imperative, and therefore it’s no longer a back-end issue—it is a board question.”
Additionally, the cost structure of commercial AI infrastructure introduces the risk of AI Distributed Denial of Service (AI DDoS) attacks, which target operational budgets rather than network bandwidth.
“The outcome of AI DDoS is very different from traditional network DDoS,” Hu points out. “Traditional network DDoS is really to exhaust your resources; AI DDoS exhausts your wallet. You could use a very small prompt to generate a lot of response, and those responses will take up tokens. Every token costs something. Downtime equals a few dollars, but with undetected AI DDoS attacks, you will detect it at the end of the month when you get your bill and be shocked by it.”
Edge-level inspection and machine-speed defense
To address semantic threats, unauthorized API execution, and resource exhaustion, cloud infrastructure providers are inserting inline inspection capabilities across the network path.
“AI operates at machine speed, so having this defense-in-depth allows us to parallelize our ability to defend and literally have unlimited scale,” Hu says. “Speed is a friction point for a lot of security solutions; a lot of people tend to give up performance for security. But from Akamai’s perspective, it is mutually a priority. From a business perspective it is a mandate, and from a security perspective you also need to be secure.”
To keep pace with rapidly evolving threat vectors, Akamai actively incorporates AI internally while participating in broader industry research initiatives.
“We see ourselves and the risks that AI brings to our organization,” Hu concludes. “We are part of the Glasswing Project and the Daybreak Project because we want to be at the edge of development as this landscape moves too fast. Akamai wants to use our 27 years of experience to help secure the current era of security.”
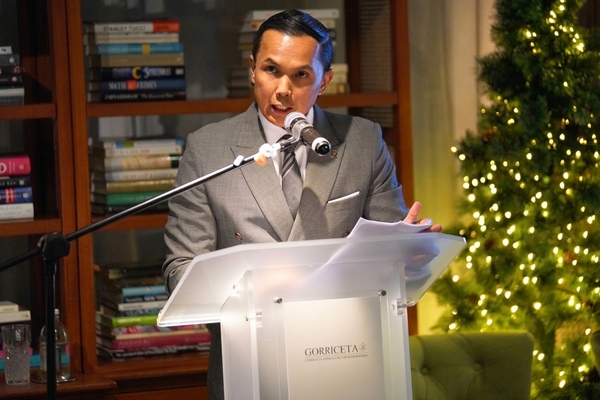
Leave a Reply